API Access
Generate secure tokens, expose your Content API endpoint and control public availability.
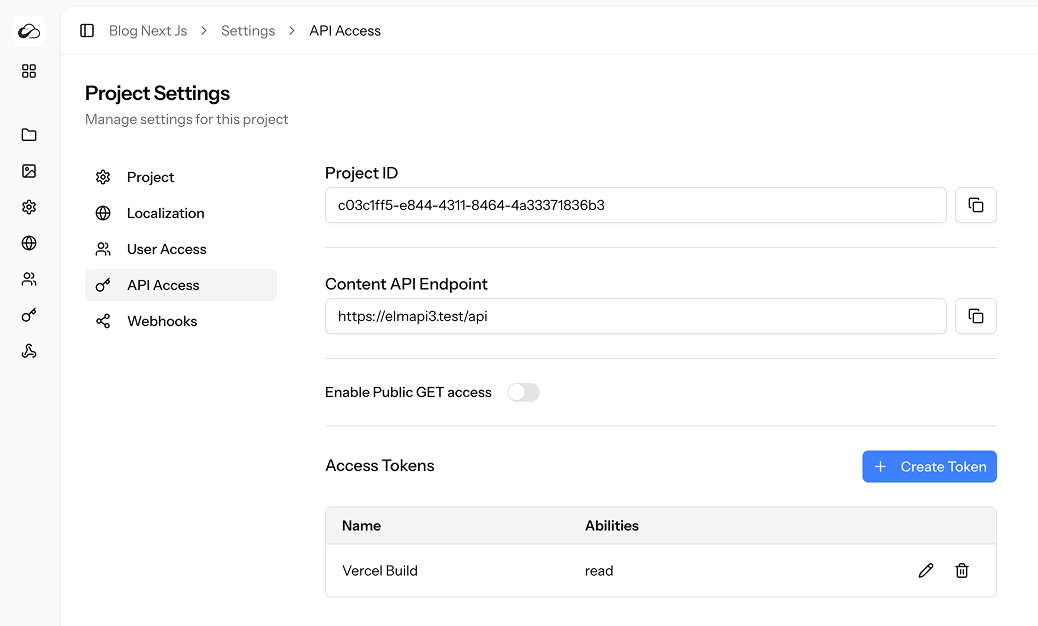
Project ID & Endpoint
| Field | Description |
|---|---|
| Project ID | UUID identifying this project in every API request. |
| Content API Endpoint | Base URL for all REST calls – normally <your-domain>/api. |
Click the copy button to put the value on your clipboard.
Public GET Toggle
Enable Public API to allow unauthenticated GET requests for content.
- When ON:
readis implied – no token required for GET endpoints. - When OFF: every request needs a token with the
readability.
Regardless of this toggle, POST/PUT/DELETE always require token abilities.
Access Tokens
| Column | Details |
|---|---|
| Name | Friendly label (e.g. “Gatsby Build”). |
| Abilities | Comma-separated list of scopes. |
| Edit / Delete | Pencil / Trash icons. |
Creating a Token
- Click Create Token.
- Enter a name and tick one or more Abilities:
read– GET endpointscreate– POST / uploadupdate– PUT/PATCHdelete– DELETE
- Copy the generated token – you won’t see it again. Store it securely.
Editing or Deleting
• Edit lets you rename the token or adjust abilities.
• Delete revokes the token immediately.
Token Abilities Matrix
| Ability | Endpoints allowed |
|---|---|
read | GET /api/files, GET /api/collections, GET /api/{collection} etc. |
create | Upload new assets, create content. |
update | Update content or metadata. |
delete | Delete assets or content. |
Permissions
| Ability | Needed for |
|---|---|
access_api_access_settings | View tab, manage tokens, toggle public API |
Best Practices
- Use separate tokens for build servers, staging and production.
- Grant the least privileges needed – e.g. a read-only token for SSGs.
- Rotate tokens regularly and delete unused ones.
- Keep tokens secret; they grant the same rights as the user who created them.